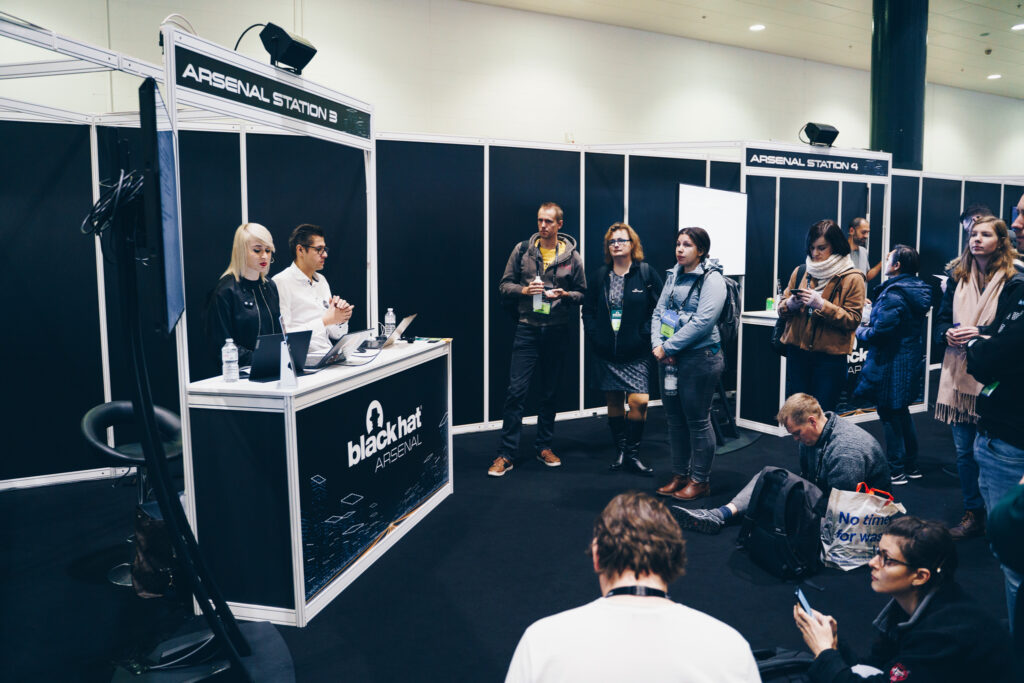
Today Paula Januszkiewicz and Mike Jankowski-Lorek presented CQURE’s forensic toolkit during the Arsenal session at Black Hat Europe 2019 in London. Find the description and tools below! CQForensic: The Efficient Forensic Toolkit CQForensic Toolkit enables you to perform detailed computer forensic examinations. It guides you through the information gathering process providing data for analysis and […]
If you have any questions please drop us a message via our contact form.
CQLabs – Offline Attacks on Active Directory Introduction This lab will guide you through some of the most interesting features of the DSInternals PowerShell Module, which was featured at Black Hat Europe 2019 and is also included in FireEye’s Commando VM. This open-source toolset exposes many internal and undocumented security-related features of Active Directory (AD), […]
Here it is – the very special interview from #BHEU 2019, led by our best journalist on board, Mike Jankowski-Lorek. 🎤 We had the opportunity to talk to Michael Grafnetter right after his keynote session and find out more about his Windows Hello for Business. Are you curious how this password-less authentication tool works? Watch the video and […]
Antivirus software usually uses malware signatures, behavioral detection or heuristic detection to block malware. All these methods may be insufficient in case of APT (Advanced Persistent Threat) attacks prepared specifically for the victim or attacks exploiting 0day vulnerabilities in software, that were never seen before. Exploit Guard: Exploit Protection and Exploit Guard: Attack Surface Reduction […]

Today Paula Januszkiewicz and Mike Jankowski-Lorek presented CQURE Academy’s forensic techniques at the Security Mashup Session at the RSA Conference 2020 in San Francisco. Find the description, slides, and tools below! Explore Adventures in the Underland: Forensic Techniques Against Hackers Evading the Hook Cybercrime is a very lucrative business not just because of the potential […]
The webinar will start at 7 PM CET here on the 26th of March 2020. If you experience any issues during the live session, please reload the page. For any questions during the webinar, please use the comments section below.
Previously on CQLabs This article is a continuation of a previous one, called #CQLabs 5 – DSInternals PowerShell Module. Introduction One of the lesser known features of Active Directory (AD) is called Credential Roaming. When enabled, it synchronizes DPAPI Master Keys, user certificates (including the corresponding private keys) and even saved passwords between computers. We […]
We have gathered some essential facts about remote working security, as it may have some challenges to overcome. Check out our new poster and discover tips that will help you to keep your home office (or wherever you work from) safe. Download the poster below! 1. There are always some IT knights in the […]
The webinar replay will start here at 7 PM CEST | 1 PM EDT | 10 AM PDT | 1 AM SGT on the 6th of MAY 2020. If you experience any issues during the live session, please reload the page. For any questions during the webinar, please use the comments section below.